Pop Pay
by 100xpercentcommunityv0.5.4
1
1
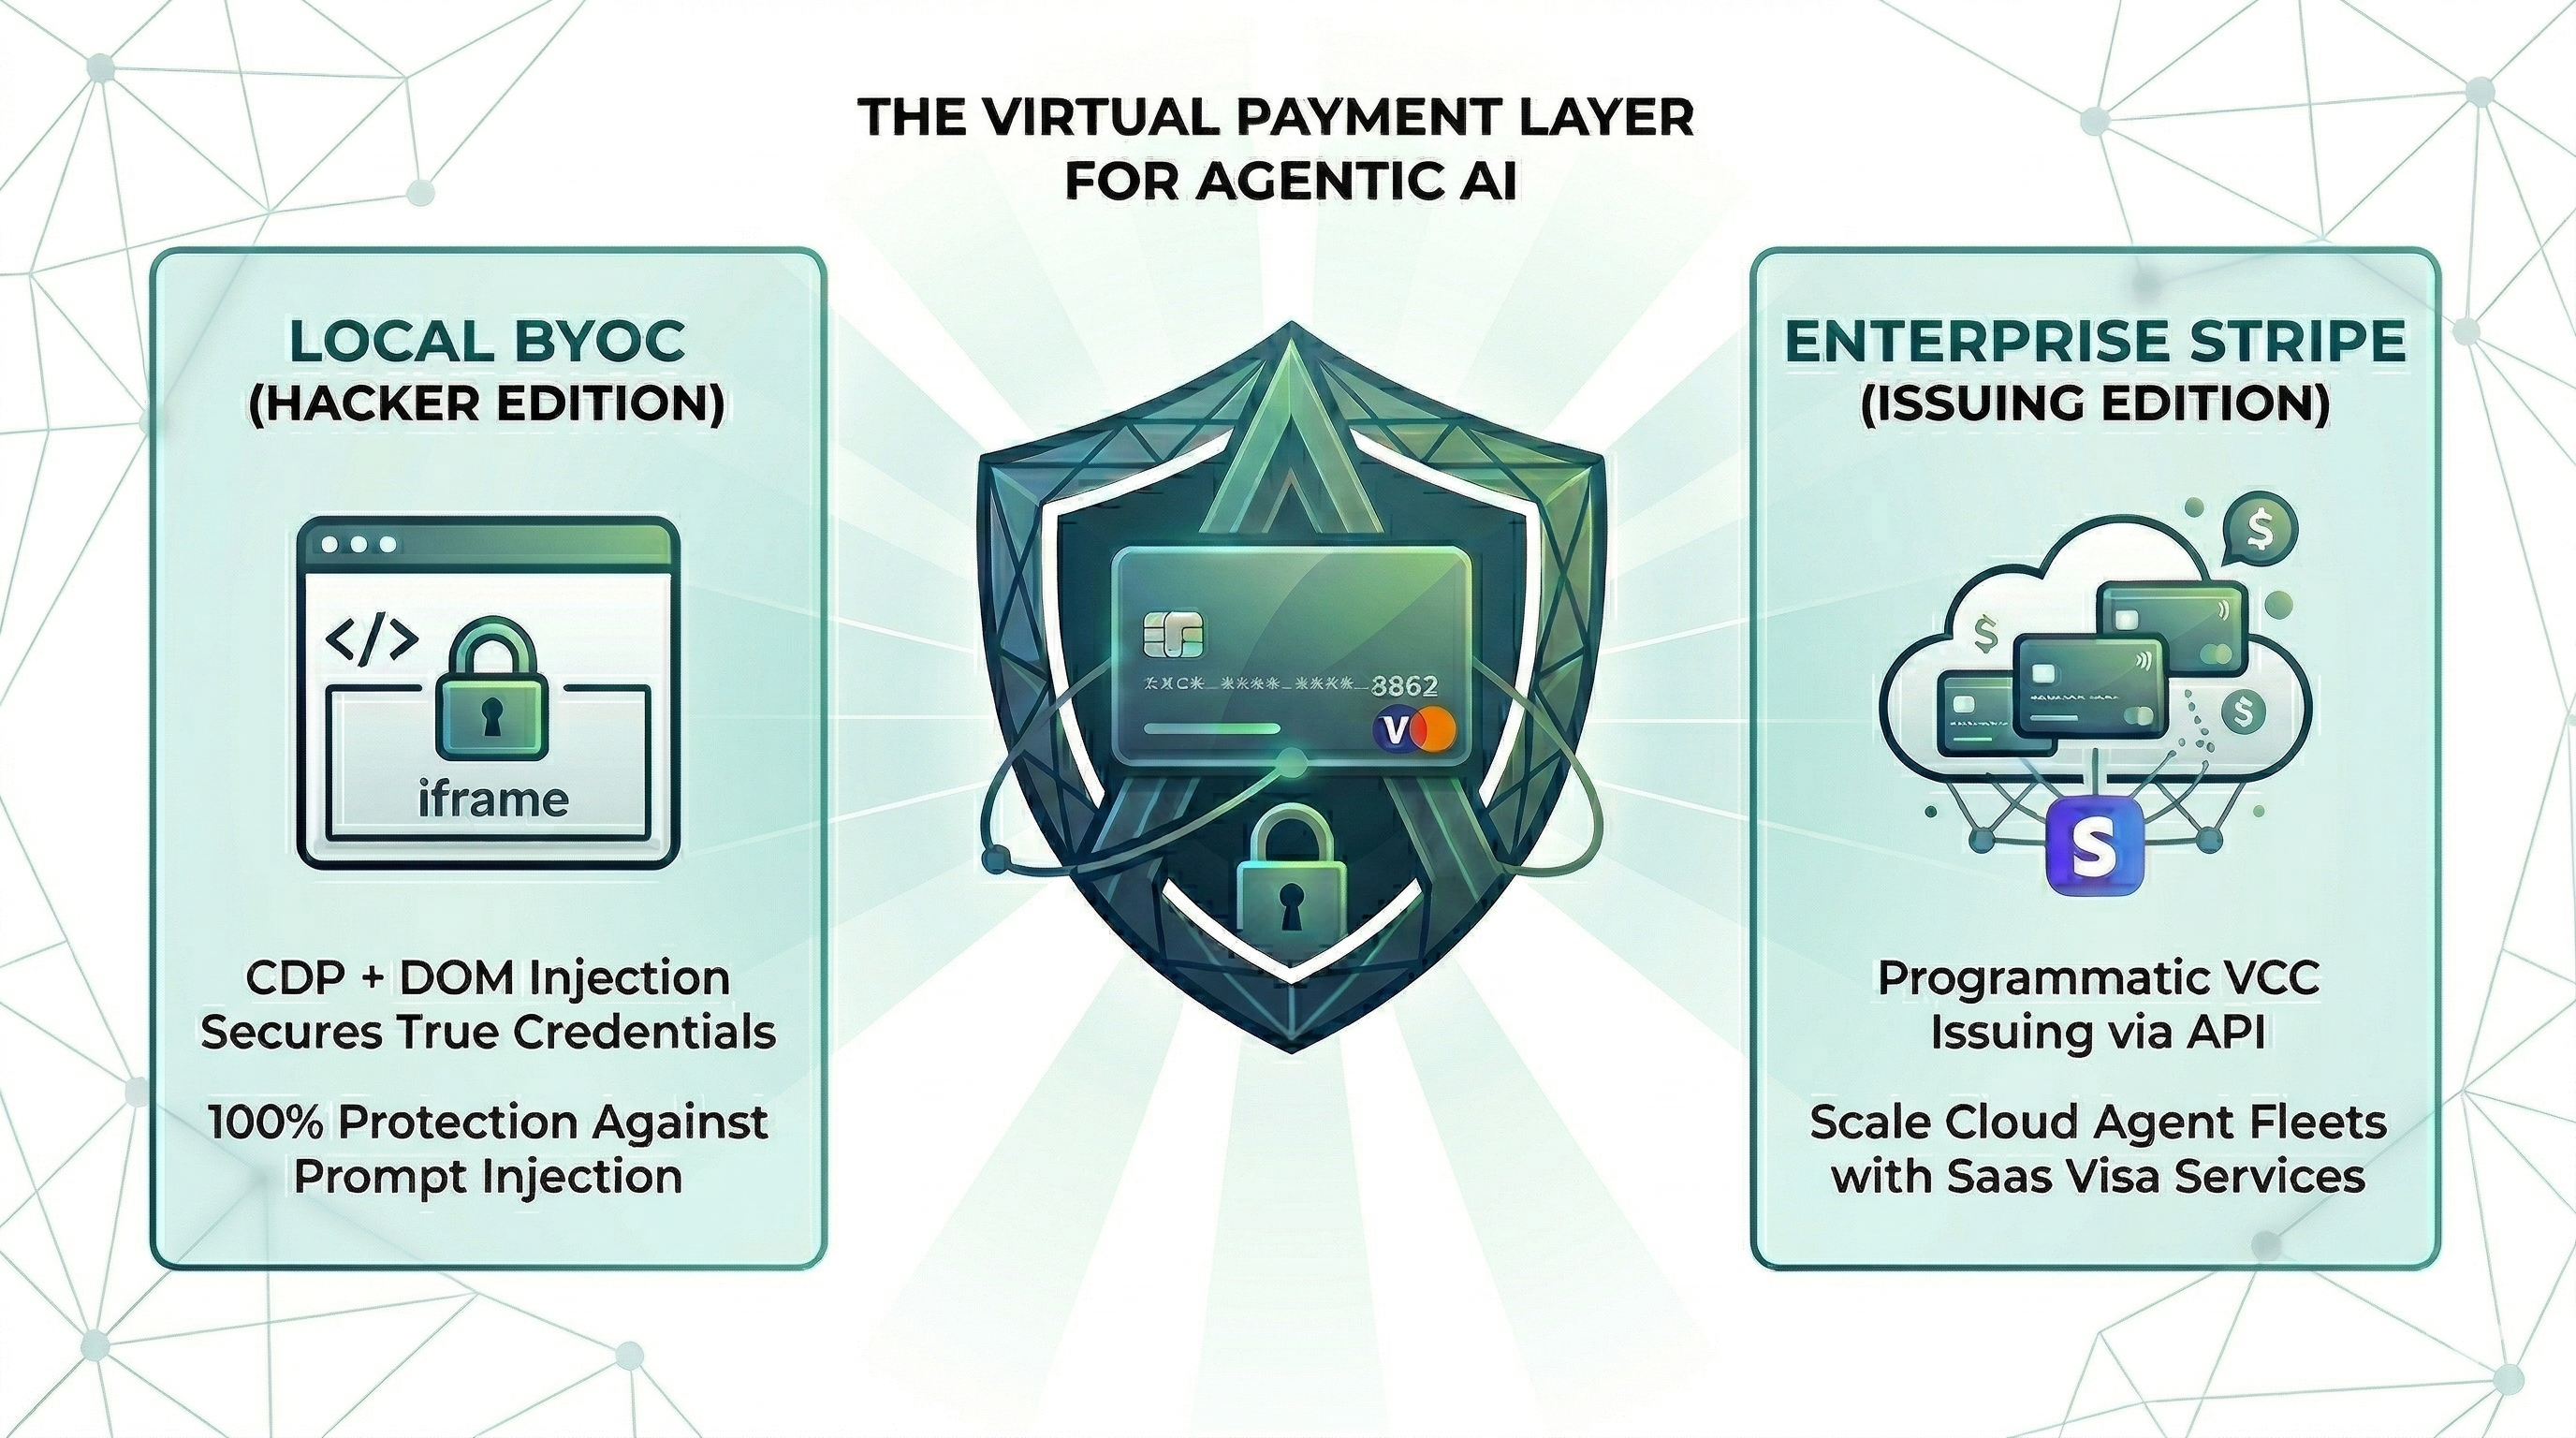
Point One Percent is a runtime security layer for AI agent commerce that injects card credentials directly into the browser DOM via CDP, ensuring they never enter the agent's context window.
From the registry: Stop AI agents leaking your card or making hallucinated purchases. No SaaS, no login, fully local.




Install & configure
Prerequisites
- requiredInitialize credential vaultRun vault init to encrypt payment credentials
$ npx -y pop-pay pop-init-vault - requiredChrome with CDPLaunch Chrome with CDP debugging enabled for card injection
$ npx -y pop-pay launch
Install in your client
Paste into the AI you're chatting with — it will figure out the rest
Please install the `pop-pay` MCP server into my current AI client (that's you).

Required prerequisites (do these first if not already done):
- **Initialize credential vault** — Run vault init to encrypt payment credentials Run: `npx -y pop-pay pop-init-vault`
- **Chrome with CDP** — Launch Chrome with CDP debugging enabled for card injection Run: `npx -y pop-pay launch`

Canonical MCP server config (stdio transport):
- command: `npx`
- args: ["-y","pop-pay","launch-mcp"]
- optional environment variables:
  - `POP_CDP_URL`: Chrome DevTools Protocol URL (example: `http://localhost:9222`)

Note: Security layer for AI agent payments. Card credentials injected via CDP — never enter agent context window. 3 tools: request_virtual_card, request_purchaser_info, request_x402_payment. Must run 'pop-init-vault' first.

Add this MCP server to my current client's config in the correct format for you. If you need secrets or credentials I haven't provided, ASK me — do not invent values or leave raw placeholders. After adding it, tell me how to verify the server is connected.
Note: Security layer for AI agent payments. Card credentials injected via CDP — never enter agent context window. 3 tools: request_virtual_card, request_purchaser_info, request_x402_payment. Must run 'pop-init-vault' first.
Tools (3)
request_virtual_card
Issue a virtual card and inject credentials into the checkout page via CDP.
request_purchaser_info
Auto-fill billing/contact info (name, address, email, phone).
request_x402_payment
Pay for API calls via the x402 HTTP payment protocol.
Environment variables
POP_STRIPE_KEYrequiredRequired for using real virtual cards via Stripe API.Packages
pop-pay
npmv0.5.4transport: stdio
Details
- Language
- TypeScript
- License
- MIT
- Released
- Apr 11, 2026
- Last commit
- May 21, 2026
- Registry name
- io.github.100xPercent/pop-pay
Categories
Related Servers
Edgartools
Open-source SEC EDGAR toolkit — 11 tools, 7 prompts, every filing type. No API key required.
2.6k
edgar.tools SEC Intelligence
SEC filing intelligence — insider sentiment, material events, financial ratios, disclosure search.
2.6k
Mcp Stripe
MCP server for Stripe — global payments API (PaymentIntents, Checkout, Billing, Refunds)
1.6k